
Sentience Governor — Security skill for Claude Code
Local-first runtime governance for AI agents.
How to install Sentience Governor
This entry records only its repository, not the path inside it, so there is no
exact command to give. Open crescerelabs/sentience-governor and copy the folder into
~/.claude/skills/, or the file into ~/.claude/agents/.
What Sentience Governor does
Local-first runtime governance for AI agents. Declare intent, catch out-of-scope actions, and audit them in a verifiable trail.
Alternatives in Security
- Maestro Knowledge — Intent-driven knowledge-store and Run knowledge lifecycle management — audit/prune, stage candidates (with sig 530 ★
- Loongsuite Pilot — Local-first telemetry collector for AI coding agents — unified OpenTelemetry events for Claude Code, Codex, Cu 150 ★
- Sovereign Skills — 20 production-grade skills for AI coding agents — setup, scope, discipline, code review, security, session man 125 ★
README
Sentience Governor
**Local-first governance for AI agents at runtime.**
Sentience Governor captures agent actions at the execution boundary, evaluates them against declared intent, scope, and policy, and writes a verifiable local record of each captured tool call.
When an agent operates outside what it declared, Sentience surfaces the policy violation and attributes the associated token usage to the turn where it happened.
[](https://pypi.org/project/sentience-governor/) [](https://pypi.org/project/sentience-governor/) [](https://github.com/crescerelabs/sentience-governor/blob/main/LICENSE) [](https://github.com/crescerelabs/sentience-governor/actions/workflows/test.yml)
No account, no API key. By default, your traces stay on your machine.
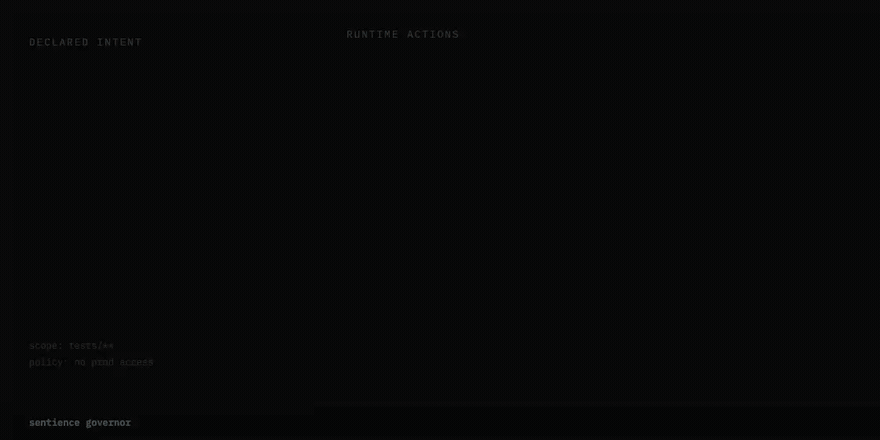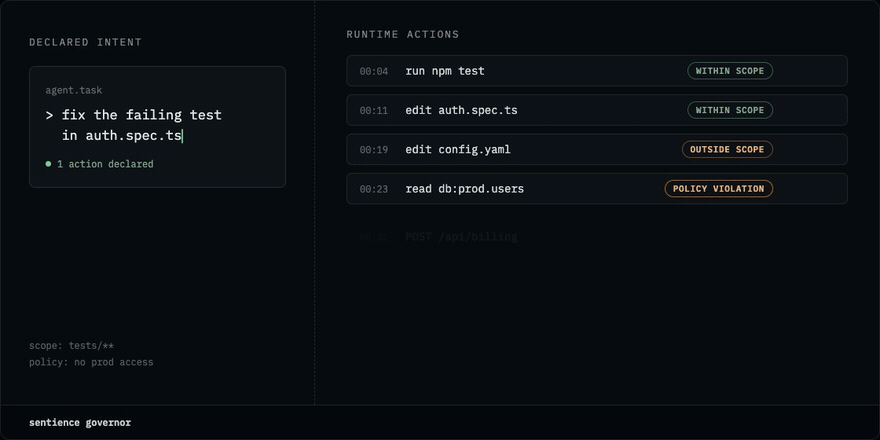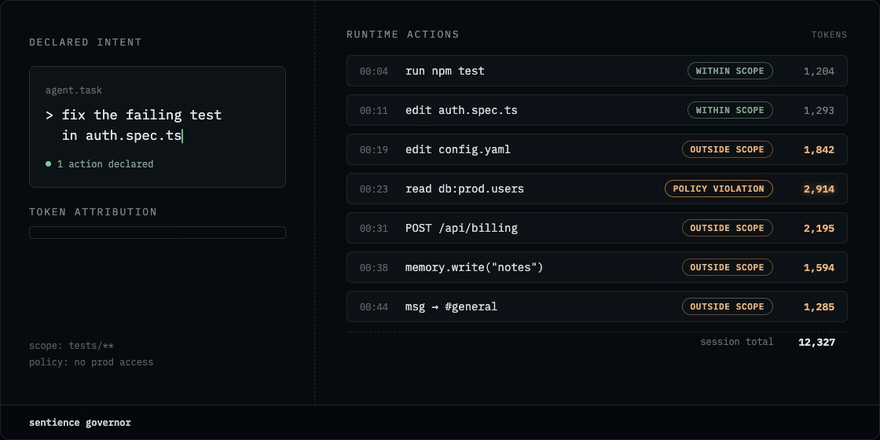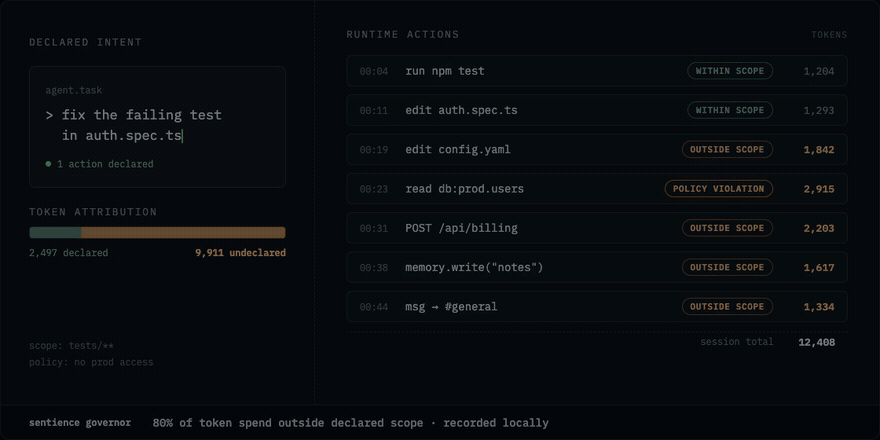
*Illustrative. Sentience records and evaluates a session, then reports on it; the open-source release does not adjudicate or block actions as they happen. For real output, see [See it work](#see-it-work) below.*
What's new
**0.3.1** adds `sentience scan` — a retrospective review of the Claude Code history already on your machine. It reports which sessions recorded write activity outside the project they were working in, before you have declared an intent or instrumented anything. Local and read-only: no signup, no network request, and no writes of any kind. The same review is available inside Claude Code as `/sentience-review`.
Related Skills
Securevector AI Threat Monitor
Security & Observability for AI Agents — audit every tool call, enforce allow/block policies, catch prompt inj


Traceary
Local-first session log and audit trail for AI coding agents (Claude Code, Codex, Gemini)


Ship Check
End-of-session production audit with auto-merge. Reconstructs session intent, then RUNS the full review chain

Managed MCP Doctor
Audit Claude Code MCP governance drift, catch when allowedMcpServers no longer covers managedMcpServers (2.1.2


Walkthrough Nt
Role-driven browser walkthrough — identify each user role, drive the running app through their journeys in a r

Openclaw Gatewaystack Governance
Superseded by openclaw-acp-plugin. Policy layer for OpenClaw: identity, scope, rate limits, audit.

Related Agents
Intent Guardian
Checks whether a change or proposal fits INTENT.md goals and non-goals. Use before starting a feature and afte

Kimi Worker
Forward a coding, diagnosis, or review task to Kimi K3 (Moonshot) through the local kimi-worker.sh runtime. Us

CI Local Runner
Use this agent to run a repo's CI gates locally and report whether the code is safe to push — especially when
