
Package Doctor — Development skill for Claude Code
Scan Python dependencies for exploited CVEs and abandoned packages that handle untrusted input, ranked by CISA KEV and EPSS.
How to install Package Doctor
This entry records only its repository, not the path inside it, so there is no
exact command to give. Open binuka200/package-doctor and copy the folder into
~/.claude/skills/, or the file into ~/.claude/agents/.
What Package Doctor does
Scan Python dependencies for exploited CVEs and abandoned packages that handle untrusted input, ranked by CISA KEV and EPSS. Runs in CI and as a Claude Code hook.
Alternatives in Development
- Rank — /rank - Triage Scraped Jobs into a Ranked Shortlist 36.6k ★
- Gemini CLI Foundations — This repository is a comprehensive skills library for Gemini CLI - reusable, production-ready skill packages t 5.3k ★
- Breach Check — HIBP k-anonymity check on a password wordlist 4.5k ★
README
package-doctor
[](https://github.com/binuka200/package-doctor/actions/workflows/ci.yml) [](https://pypi.org/project/package-doctor/) [](https://pypi.org/project/package-doctor/) [](https://github.com/binuka200/package-doctor/blob/main/LICENSE)
**Tells you which Python dependencies to fix first: the ones being exploited, and the ones nobody is left to patch. Then stops your coding agent from adding another.**
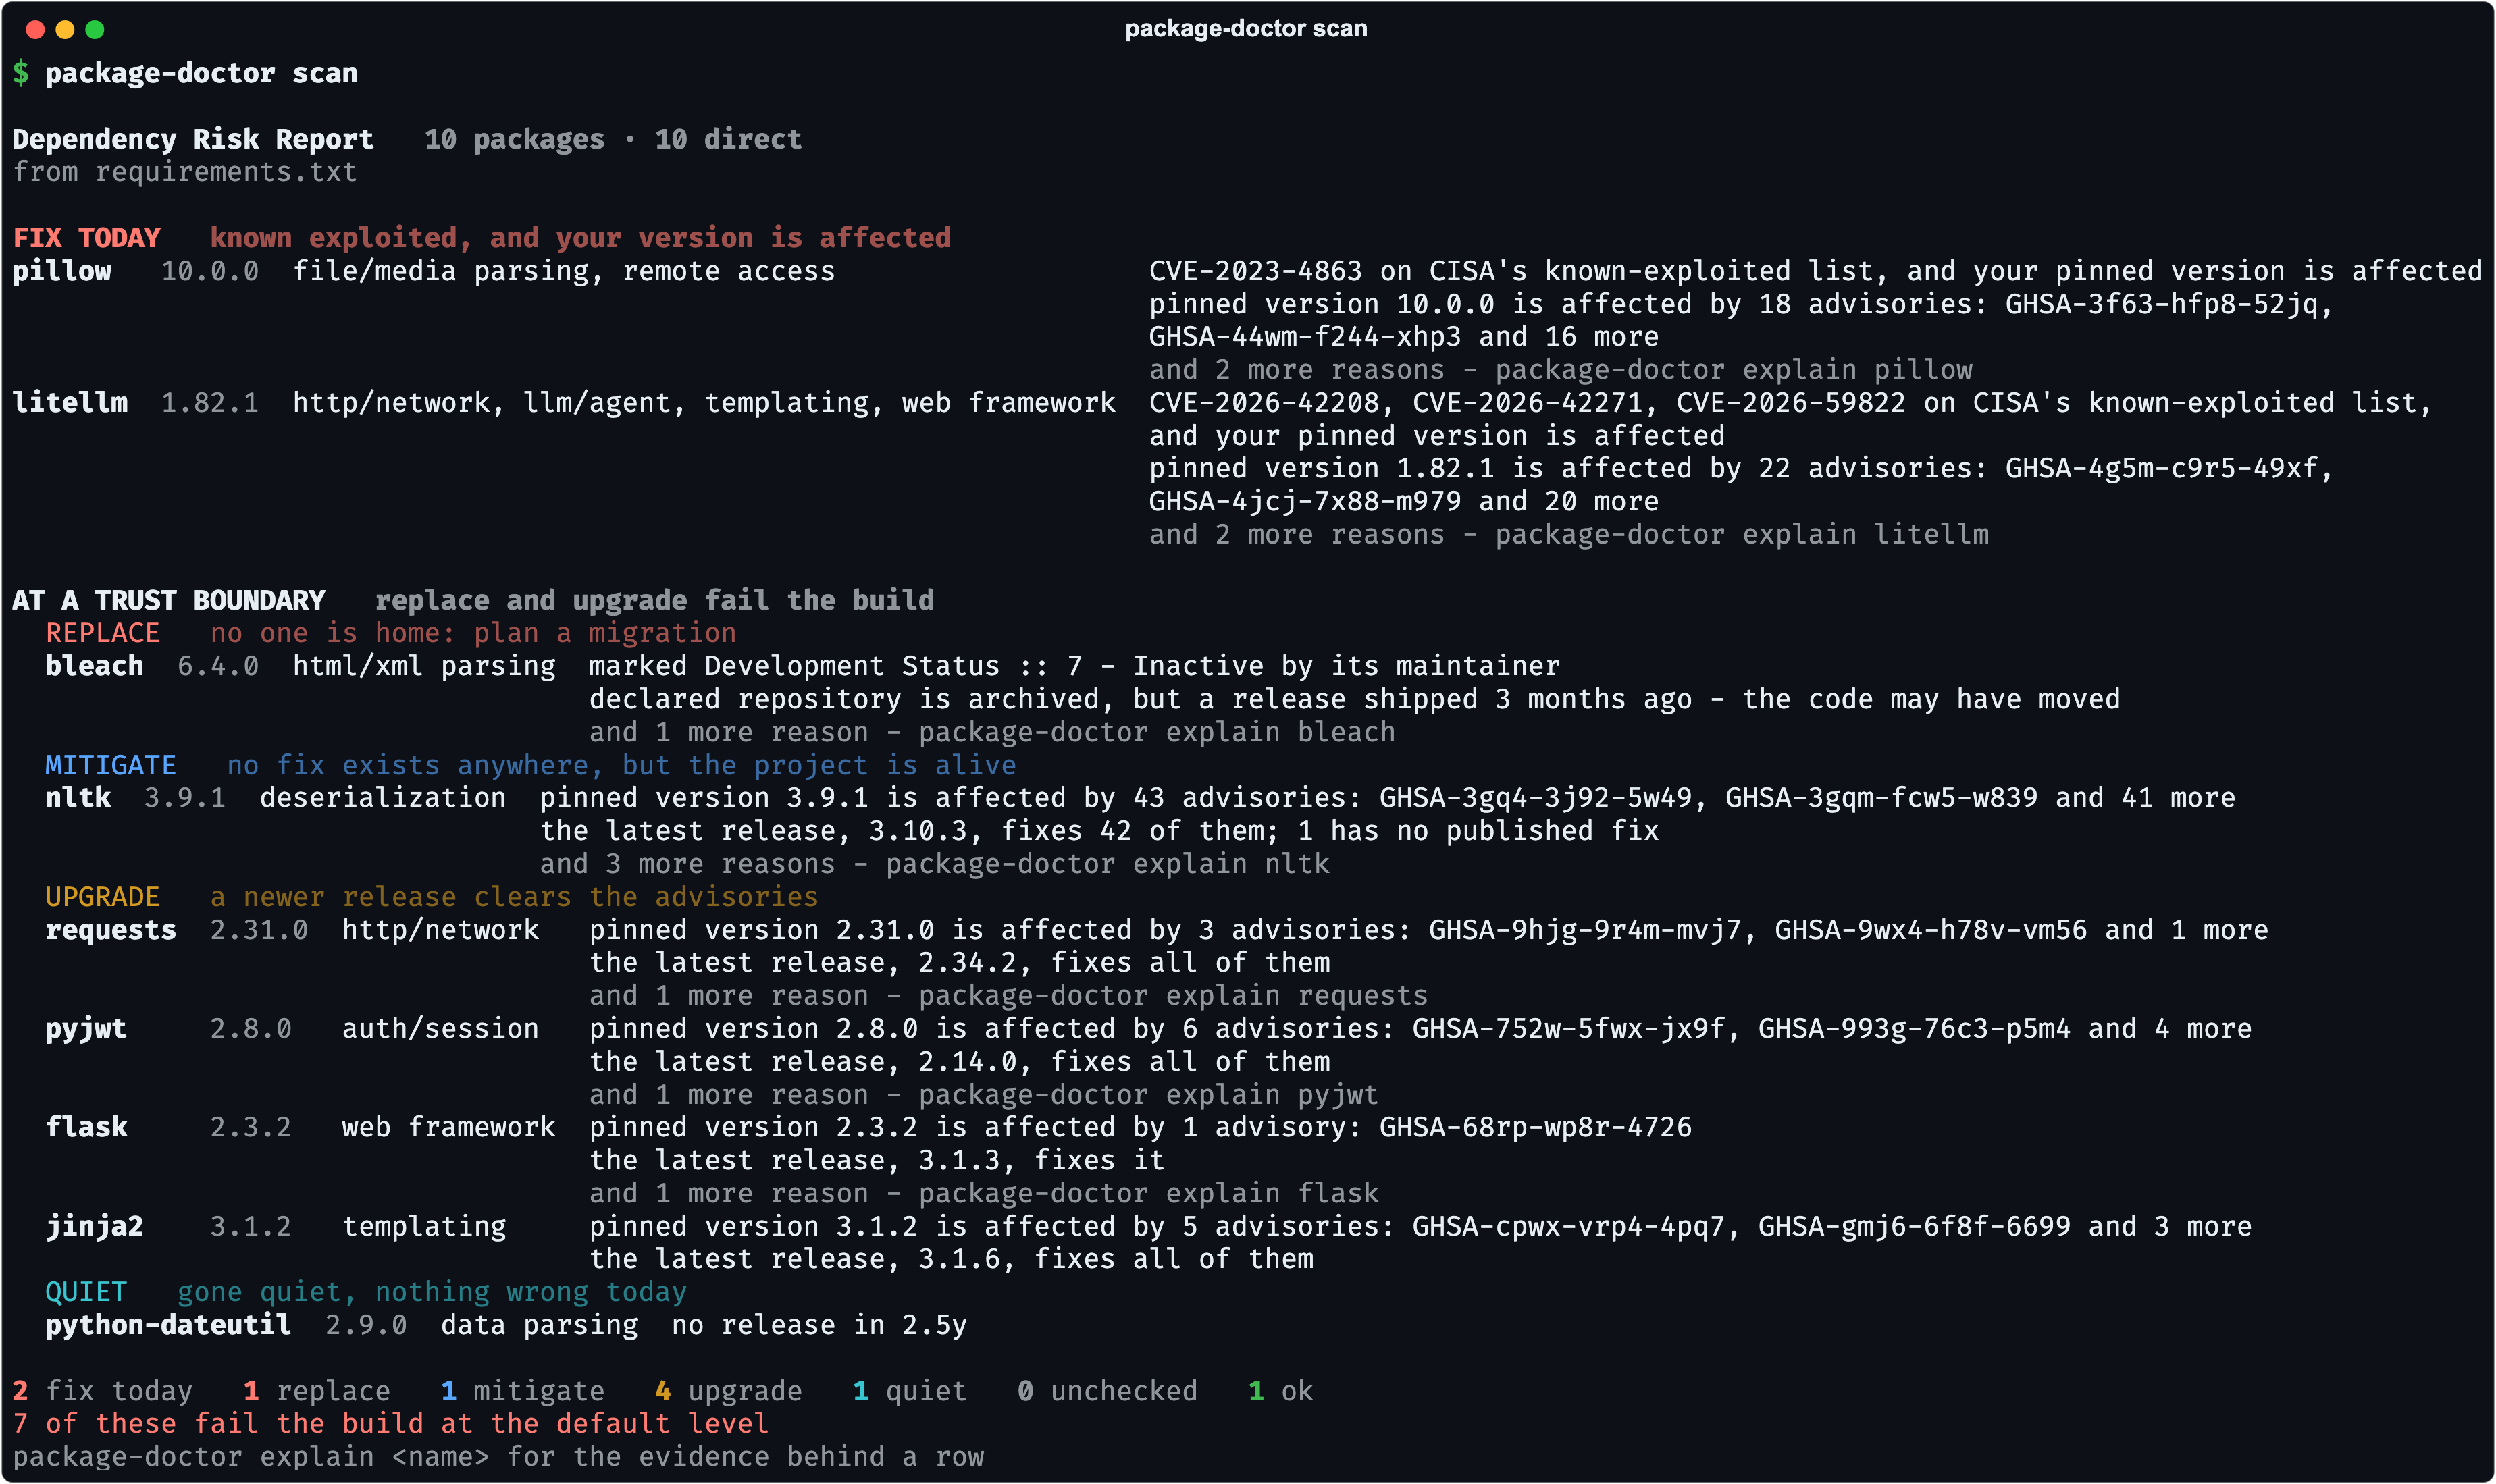
A demo project with deliberately old pins, scanned on 16 September 2026. Advisory and exploitation data change daily, so the same pins will not read the same later.
In late August 2026, Anthropic's coordinated disclosure programme reported 2,300 vulnerabilities across 392 open source projects. 421 had been patched upstream. Discovery is becoming automated; remediation still needs a human. So the question worth asking about a dependency is not *"is it healthy?"* It is:
**If a vulnerability lands in this package tomorrow, am I exposed, and is anyone home to fix it?**
What it does
- Two axes, not one. A package is escalated only when it sits at a trust
boundary - it parses, decodes or authenticates data an attacker can
influence - and there is proof nobody is left to ship a fix.
mockgoing quiet is not a finding; an archived auth library is. The
Related Skills
Heeler Malicious Package Scan
Detect suspicious or malicious dependencies using Heeler package-risk intelligence. Use when a new dependency


Ohd Checkup
Harness doctor for an existing project — 하네스 점검/정비/채택. Detects drift between the project and the ohd harness (


MCP Tactics
Claude Code Skill: cross-cutting tactics book for nlink-jp's MCP servers — decision tables from input artifact


Automation Publish
Automation Package Publishing Command - Publish both orchestration and automation packages to PyPI


Add Package
Adds packages to pubspec.yaml with proper configuration and setup

Skilldex
Package manager and registry for Claude skill packages - install, validate, score, and publish .skill packages

Related Agents

Dep Auditor
Use to audit project dependencies for known CVEs, abandoned packages, license incompatibility, and significant


Ecosystem Maintenance
Periodic health sweep across all Zanix repos for outdated/deprecated third-party dependencies (Deno std, npm p

Security Tester
Use to audit code and dependencies for security problems - injection, auth and authorization gaps, secret leak
